Shared Principles, Divergent Paths: Pingping Huang on Why AI Governance Is Fragmenting Across Borders
Q1. Can you tell us about the Center for United Nations Constitutional Research (CUNCR) — its origins, its focus on UN Charter reform and multilateral institutional design, and why a think tank grounded in constitutional questions about the UN itself is now turning its attention to AI governance? What made CUNCR decide that AI governance is fundamentally an institutional and constitutional challenge rather than simply a technology policy problem?
CUNCR is an independent, not-for-profit think tank based in Brussels. It focuses on research and civil society work on UN reform, peace and security, and global governance. Its main mission is to study the UN Charter, and to make policy recommendations. A central idea behind this work comes from the opening words of the Charter: “We the peoples.”
CUNCR examines whether the present United Nations system is capable of addressing today’s global challenges. A central focus of its research is Article 109 of the UN Charter, which provides for a General Conference to review the Charter. Of particular importance is Article 109(3)—the heart of what CUNCR calls the “San Francisco Promise.” Paragraph 3 required the question of convening such a conference to be placed on the agenda of the General Assembly’s tenth annual session if no conference had yet been held. In 1955, both the General Assembly and the Security Council approved holding a review conference, yet it was never convened. CUNCR seeks to restore this neglected constitutional commitment to contemporary debates on UN reform. The research is developed in the recent book by CUNCR’s founder, Dr. S.M. Sharei, and in his article published by Lawfare. The essential point is that meaningful institutional reform need not begin outside the Charter: the Charter itself contains an agreed mechanism for its comprehensive review.
Article 109 does not provide an answer to AI governance. But it leads to a wider question: are the mandates and structures of existing international institutions still suitable for new global problems? AI governance is often discussed through national laws, technical standards, and company compliance. These are important. But a basic question remains unanswered: who is responsible for AI governance at the global level?
An AI system may be developed in one country and deployed in many others. Its effects may cross national borders. National and regional rules can regulate activities within their own jurisdictions, but they cannot address every cross-border issue. This makes AI governance an institutional question. It is also constitutional in a broader sense. Here, “constitutional” concerns the basic rules for public authority. Who has the authority to make decisions, and how should that authority be limited? Who should bear responsibility when an AI system causes harm? For this reason, CUNCR treats AI governance not as a new problem, but as part of its long term work on effective global governance, fit for the global existential challenges.
Q2. Your research asks a question that most AI governance discourse avoids answering directly: which multilateral institutions, if any, actually have the mandate, capacity, and legitimacy to govern AI at the global level? Based on what you observed representing CUNCR at the inaugural UN Global Dialogue on AI Governance in Geneva, what is your honest assessment — is there currently any institution positioned to fill that role, or are we watching a genuine institutional vacuum that competing national and regional frameworks are rushing to fill?
My assessment is that no existing multilateral institution has the full mandate, capacity and legitimacy to govern AI globally. The United Nations is suitable to coordinate this work because its universal membership allows almost every country to take part.
However, the UN Global Dialogue on AI Governance is a platform for discussion and cooperation. It cannot adopt binding global rules, supervise national regulators or enforce rules on companies. The Independent International Scientific Panel on AI can provide scientific assessments, but it is not a regulatory body. UNESCO works on AI ethics, while the International Telecommunication Union contributes to technical standards and capacity-building. These roles are important, but they cover specific functions.
My main impression from the Global Dialogue in Geneva this July was not that institutions were absent. The problem was divided responsibilities and limited coordination. The sessions I followed also showed different priorities. Some focused on advanced AI safety, technical standards and national regulatory models. Others focused on infrastructure, skills, capacity-building, parliamentary oversight and whether developing countries can take part in shaping the rules.
I would therefore not describe the current situation as a complete institutional vacuum. Many institutions and initiatives already exist. But no single institution has overall authority or responsibility for global AI governance. National and regional frameworks are trying to fill this gap, but they cannot provide global coordination. There is also no common international process for dealing with AI-related harm that affects several jurisdictions.
The United Nations does not need to be a global regulator to govern AI. National and regional authorities would continue to regulate within their jurisdictions. Specialized organizations would work within their mandates. The United Nations could provide an inclusive forum for coordination and help reduce conflicts between different frameworks.
The first Global Dialogue is an important beginning. The next question is whether it leads to clearer responsibilities, better coordination and practical follow-up before the second Dialogue in New York in May 2027.
Q3. Jurisdictions across the EU, US, China, and South Korea often converge on similar high-level principles — safety, transparency, human oversight, accountability — yet diverge sharply in how those principles become binding law and institutional practice. Drawing on your comparative work across EU, Korean, and Chinese regulatory approaches, what is the deepest source of that divergence — is it primarily legal tradition, political economy, differing conceptions of the state’s role, or something else — and where do you see the gap between shared principles and divergent implementation creating the most friction for businesses operating across borders?
I do not think legal tradition alone explains the divergence. I have spent more than 15 years working on cross-border legal and compliance matters in Shanghai and Seoul, together with my academic research in public international law. This experience has shown me that agreement on a principle does not mean agreement on its practice sand legal effect.
The deeper difference is how each jurisdiction balances the role of the state and what it expects regulation to do. The EU has adopted risk-based rules that apply across sectors. It places strong emphasis on fundamental rights, safety and the internal market. The United States has a more decentralized approach. It relies on sector-specific rules, existing laws, federal and state authorities, and voluntary frameworks such as the NIST AI Risk Management Framework.
China gives the state a central role in both supporting and supervising AI development. Its approach also connects AI with personal information protection, data security, cybersecurity, national security, and online content. South Korea seeks to promote its AI industry while setting duties for high-impact and generative AI under its AI Basic Act. These systems do not simply differ in how strict they are. They begin with different legal structures and policy priorities.
In my experience, classification is often the first practical difficulty for a company operating across borders. The same AI system may need to be assessed as high-risk in the EU or high-impact in South Korea. In the United States, the relevant rules may depend on the sector and the state. In China, separate rules on algorithms, data and content may also apply.
The principles may look similar, but the evidence required to show compliance is different. Companies may need different risk assessments, notices, labels, records and internal procedures. Work completed in one jurisdiction may not satisfy another.
Complete harmonization is unlikely. In practice, companies need regulators to recognize comparable assessments and safeguards across jurisdictions. This could reduce repeated compliance work.
Q4. You have spent over 15 years working on cross-border legal and compliance matters in China and South Korea, both in-house and in law firm settings, covering fintech, digital assets, AI, and data governance. That practical experience gives you a vantage point that most academic AI governance researchers lack — you have seen how frameworks are actually interpreted, implemented, and enforced, not just how they are written. What is the most significant gap you have personally observed between the formal language of an AI or data governance regulation and how it actually plays out in practice for a company trying to comply with it?
The most significant gap I have seen is between a legal requirement and the internal process needed to comply with it. A law may require transparency, accountability, data protection or human oversight. These requirements may appear clear at a general level. But a company still has to decide how to apply them, who is responsible and what evidence is needed.
This becomes more difficult in cross-border business. Data may be collected in one country, processed in another and used to provide a service in a third. A decision made at headquarters may affect users and business partners in several jurisdictions. The applicable rules do not always fit together. It may also be unclear whether responsibility belongs to the developer, deployer, local subsidiary or service provider.
In my work, business teams usually needed answers to practical questions. Can we launch this service? Can we transfer the data? What must we explain to users? What should we document if a regulator later asks questions? The formal rule rarely answers all of these questions directly.
Compliance therefore does not end with a written policy. Legal, compliance, product and technical teams must decide how the rule will be applied and who is responsible for each step. They also need records showing what was done. Without this, a company may have a good policy on paper but still be unable to show how it was followed.
The gap becomes clear when a regulator or user asks how an automated decision was made. The company must know who will answer the question and which records support the explanation.
Q5. You are extending your earlier peer-reviewed research on the role of regional organizations in shaping due diligence norms in cyberspace into the domain of AI governance. What does that cyber governance precedent teach us about how regional frameworks — the EU AI Act, ASEAN’s approach, or others — might eventually shape or constrain global AI governance norms, and do you see AI governance following a similar trajectory to cyber norms, or is AI different in ways that make that comparison misleading?
My earlier research examined how the EU, the Organization of American States and the African Union approached cyber due diligence. My main finding was that regional organizations can do more than repeat global principles. They can bring national positions into regional discussions, develop common positions and help clarify disputed legal concepts. Their work can also support the United Nations when it seeks wider agreement.
In some circumstances, regional practice may also contribute to the development of customary international law. But a regional statement cannot create customary international law by itself.
I see part of the same process in AI governance. The EU AI Act is binding and risk-based. It can also apply to companies outside the EU when they place AI systems on the EU market or when the output of their systems is used in the EU. Its influence may go further through what is often called the “Brussels Effect.” Some companies may apply EU requirements more widely rather than operate a separate compliance system only for the EU market. The ASEAN Guide on AI Governance and Ethics is voluntary. It encourages regional alignment and interoperability while leaving room for different national approaches.
There is also an interesting difference from my cyber law research. At that time, ASEAN had not adopted a common position on cyber due diligence. In AI governance, it has already developed a regional guide. This shows that regional norm development does not follow the same path in every field.
AI governance may therefore follow part of the cyber trajectory. Global principles can be discussed at the international level, interpreted through regional frameworks and applied through national laws and practices. Regional frameworks can gradually build wider agreement.
But the comparison has limits. Cyber due diligence mainly concerns state obligations under international law. AI governance directly affects developers, deployers, products, data and business models. Private companies and technical standards bodies also have a more direct role. AI systems and markets change quickly. A regional AI rule can therefore influence global business practices before states reach an international legal consensus.
Regional frameworks have two sides. On one hand, they can build common ground faster than a global process. On the other hand, they can also harden into separate systems that are difficult to reconcile later. The United Nations can identify minimum protections and areas where different systems can work together. It can also help countries with limited regulatory capacity take part in shaping the rules.
Q6. You have been appointed Head of the CUNCR Delegation to COP31 in Antalya this November, where you are organizing a side event specifically on the intersection of climate change and global AI governance, focused on making AI governance more climate-friendly. That is a genuinely underexplored intersection. What is the core argument you want policymakers at COP31 to take away from that conversation — what does it actually mean, in concrete institutional or regulatory terms, to make AI governance more climate-friendly, and why does that connection matter enough to bring to a climate conference rather than an AI-specific forum?
CUNCR is a co-applicant for a proposed COP31 side event titled “Women Advancing Climate-Friendly Global AI Governance.” The event would focus on women innovators, science-based climate solutions and what global AI governance can learn from the UNFCCC and the IPCC. The final outcome is not yet known.
The core argument is that climate-friendly AI governance means more than using AI for climate action. AI can support energy management, climate modelling and disaster response. But AI systems also depend on data centres, electricity, water and other infrastructure. These costs should be considered within AI governance.
In practical terms, we need more consistent methods for measuring and reporting the energy use, emissions and water consumption of AI systems. Environmental impacts should be considered in risk assessments, public procurement and decisions about data-centre infrastructure. Responsibility also needs to be clear. Developers, cloud providers, data centre operators and deployers are responsible for different parts of the AI system. Environmental responsibility should not be passed from one actor to another.
There is also an institutional lesson from climate governance. AI governance does not need to copy the UNFCCC or the IPCC. The fields are different. The IPCC shows the value of independent scientific assessment. The UNFCCC system shows the value of common reporting, regular review and support for countries with limited capacity. For example, the UN Independent International Scientific Panel on AI could include environmental impacts in its assessments. Climate institutions and AI governance should also share information more regularly.
This issue belongs at a climate conference because the environmental effects of AI are not only technical matters. They concern electricity systems, water, emissions, infrastructure investment and a just transition. They also raise questions of equity. The benefits of AI may be concentrated in a few countries and companies. Some environmental costs may fall elsewhere, including on communities with limited energy and water resources.
COP brings together governments and climate and energy actors from countries that are often less represented in AI debates. These participants already make decisions about energy, water and infrastructure. This gives COP a direct role in the discussion about the environmental impact of AI.
Q7. Anything else you wish to add?
One point I would add is that these questions are not only theoretical. CUNCR will examine them at its research seminar, Governing AI in a Fragmented World: Brussels, Beijing, Washington – Can the UN Bridge the Gap?, on 4 November 2026 in Brussels.
The seminar will discuss why AI governance is becoming more fragmented and what the United Nations can effectively do to improve coordination. It will also consider practical questions of participation, capacity-building and accountability. We hope to bring together perspectives from different legal, institutional and regional backgrounds. My main point is that fragmentation is creating practical problems. We need to identify where coordination is possible and what the United Nations can effectively do.
References
- Center for United Nations Constitutional Research (CUNCR), “Who We Are: Statutes and Mission.” https://cuncr.org/who-we-are/
- United Nations, “United Nations Charter: Full Text,” including Article 109. https://www.un.org/en/about-us/un-charter/full-text
- ShahrYar M. Sharei, “The Future in the Past: Reconstructing Article 109(3) of the UN Charter Towards The San Francisco Promise to Constitutionalise the United Nations and International Law.” https://www.amazon.com/Future-Past-Reconstructing-Constitutionalise-International/dp/B0DD98WN1P
- ShahrYar M. Sharei, “Reviving Article 109: A Legal Path Out of Security Council Paralysis,” Lawfare. https://www.lawfaremedia.org/article/reviving-article-109–a-legal-path-out-of-security-council-paralysis
- United Nations, “Global Dialogue on AI Governance.” https://www.un.org/global-dialogue-ai-governance/en
- United Nations, “Independent International Scientific Panel on Artificial Intelligence.” https://www.un.org/independent-international-scientific-panel-ai/en
- International Telecommunication Union, “AI for Good.” https://aiforgood.itu.int/
- European Union, Regulation (EU) 2024/1689 laying down harmonised rules on artificial intelligence, “EU AI Act.” https://eur-lex.europa.eu/eli/reg/2024/1689/oj
- Anu Bradford, “The Brussels Effect,” Northwestern University Law Review, Vol. 107, No. 1, 2012, pp. 1-68.https://scholarship.law.columbia.edu/faculty_scholarship/271/
- U.S. National Institute of Standards and Technology, “AI Risk Management Framework.” https://www.nist.gov/itl/ai-risk-management-framework
- Cyberspace Administration of China, “Interim Measures for the Management of Generative Artificial Intelligence Services,” 2023. https://www.cac.gov.cn/2023-07/13/c_1690898327029107.htm
- Ministry of Science and ICT, Republic of Korea, “A New Chapter in the Age of AI: Basic Act on AI Passed at the National Assembly’s Plenary Session,” 2024. https://www.msit.go.kr/eng/bbs/view.do?bbsSeqNo=42&nttSeqNo=1071
- Pingping Huang, From Soft Law to Hard Law: The Transformation of Cyber Due Diligence in International Law – Centering on Practices of States and International Organizations, PhD dissertation, Korea University, 2025. https://dcollection.korea.ac.kr/srch/srchDetail/000000290546
- Pingping Huang, “Practices and Implications of Regional Organizations for the Consensus on the Principle of Due Diligence under International Law in Cyberspace,” Myongji Law Review, Vol. 23, No. 1, 2024, pp. 73–100. https://www.kci.go.kr/kciportal/ci/sereArticleSearch/ciSereArtiView.kci?sereArticleSearchBean.artiId=ART003107298
- ASEAN, ASEAN Guide on AI Governance and Ethics, 2024. https://asean.org/wp-content/uploads/2024/02/ASEAN-Guide-on-AI-Governance-and-Ethics_beautified_201223_v2.pdf
- International Energy Agency, Key Questions on Energy and AI, 2026. https://www.iea.org/reports/key-questions-on-energy-and-ai
- UNFCCC Technology Executive Committee, Artificial Intelligence for Climate Action in Developing Countries: Opportunities, Challenges and Risks. https://unfccc.int/ttclear/misc_/StaticFiles/gnwoerk_static/AI4climateaction/28da5d97d7824d16b7f68a225c0e3493/a4553e8f70f74be3bc37c929b73d9974.pdf
- Center for United Nations Constitutional Research (CUNCR), “Governing AI in a Fragmented World: Brussels, Beijing, Washington – Can the UN Bridge the Gap?” https://cuncr.org/research-seminars/governing-ai-in-a-fragmented-world/governing-ai-fragmented-world/
…………………………………………………………………………………………
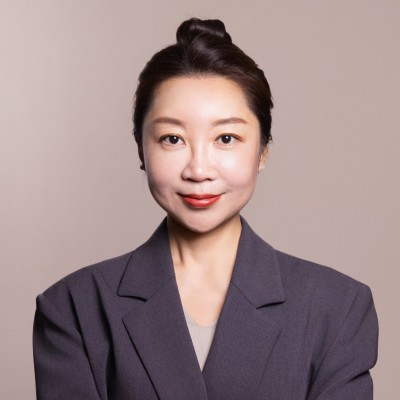
Dr. Pingping Huang is a Research Fellow at the Center for United Nations Constitutional Research (CUNCR) and an international law researcher and cross-border legal and compliance professional. Her work focuses on global AI governance, digital regulation, and comparative approaches to emerging technology law. Originally from China and now a Korean national, her perspective is shaped by experience across different legal systems, languages, and regulatory cultures.
Her doctoral research at Korea University examined the development of cyber due diligence from a soft law norm toward a binding obligation under international law, drawing on the practices of states and international organizations. She now builds on this research in her work on AI governance, particularly regulatory fragmentation and the role of multilateral institutions.
She brings 15 years of cross-border legal and compliance experience across China and South Korea, covering sectors including manufacturing, real estate, fintech, digital assets, and AI.
At CUNCR, she is developing the think tank’s global AI governance research agenda. She represented CUNCR at the inaugural UN Global Dialogue on AI Governance in Geneva in July 2026 and is coordinating its research seminar on global AI governance in Brussels. She has also been appointed Head of the CUNCR Delegation to COP31, with a particular focus on the relationship between AI governance and climate change.
She holds the AIGP and CIPP/E certifications and works in English, Korean, and Chinese. Follow her on LinkedIn.